Financial AI agents touching your files: can you explain that handoff?
Field risks
The problem: no durable record of what was handed to AI
As finance teams adopt AI agents, the following risks become visible.
KYC and AML review logs do not remain, leaving no explanation for regulator inspection.
No one can later prove which journal or trial-balance range the month-end AI touched.
It is unclear who approved giving unpublished M&A data to a pitch-book AI.
Investment materials were handed to Claude, but there is no job-level evidence of what it processed.
Supported agent patterns
Ten finance-agent patterns and how Sealith fits them
These are representative finance-agent workflows and how Sealith governs each handoff pattern.
KYC Screener
KYC Screener
Disclose customer information used by AML entity, sanctions, and PEP screening AI under a purpose, time, and domain limit, then expire it automatically after review.
Month-End Closer
Month-End Closer
Issue an Agent Token limited to accounting work when passing trial balances and journal files to month-end close AI, and prove what was processed through the audit log.
Financial Statement Auditor
Financial Statement Auditor
Limit access to BS and PL data strictly to financial statement audit purposes, with evidence export ready for outside audit firms.
Pitch Builder
Pitch Builder
Let AI build pitch books from comps and valuation data while isolating each transaction with its own token boundary.
Financial Model Builder
Financial Model Builder
Track exactly which historical financial datasets and market data the AI used when building the model.
Credit Memo / Underwriting
Credit Memo / Underwriting
Limit loan applications and credit files to underwriting purpose only, then revoke access after review to support lending explainability.
Meeting Prep
Meeting Prep
Restrict access to financial summaries prepared for investor meetings so only the IR team can use them.
Earnings Reviewer
Earnings Reviewer
Let AI review quarterly and annual disclosure packages while keeping access limited to the finance function.
General Ledger Reconciler
General Ledger Reconciler
Control ledger, bank, and evidence-file access with an accounting-only token and preserve the reconciliation trail.
Research Agent
Research Agent
Use Agent Tokens to implement fund-by-fund information barriers when investment AI researches reports and data rooms.
Before / after
Before and after governed financial AI handoff
Putting Sealith in the middle changes both explainability and audit readiness.
KYC / AML screening
Compliance and review teamPersonal data and AML compliance riskBefore
Upload customer information directly into AI, with access persisting after review and no action log.
With Sealith
Disclose under a purpose-bound, time-limited Agent Token for KYC screening, auto-expire it after matching, and trace the jobId.
Month-end close and financial statement processing
Accounting and financeInternal control gaps and retention-law riskBefore
Pass trial balances and journal data into AI without a clear record of when, by whom, and for what reason.
With Sealith
Limit access to accounting-close purpose only with an accounting AI token, and retain the trail as audit evidence.
Pitch book and DD data sharing
IB teams and M&A advisorsInsider-trading and conflict-of-interest riskBefore
Give unpublished M&A materials and valuation data directly to AI with no information barrier.
With Sealith
Issue a dedicated Agent Token per transaction with limited purpose, destination, and expiry to enforce the information barrier technically.
Submitting materials to external audit firms
CFO and internal auditAudit reliability and evidence preservation riskBefore
Use attachments or raw cloud shares with little certainty about who viewed them and when.
With Sealith
Deliver through domain-limited URLs, preserve open logs, and keep them as audit evidence.
Regulatory mapping
Technical support for finance regulations and governance guidance
Map AI handoff control to FISC-style expectations, FSA AI governance, and retention evidence requirements.
Support for FISC security standards
Apply three layers of control around AI disclosure: purpose limitation, activity records, and expiry management.
Mapping FSA AI governance topics
Use Agent Token purpose binding and audit logs as technical inputs when reviewing the FSA AI Discussion Paper's governance topics.
Evidence for e-book retention and invoicing rules
Preserve supporting transfer evidence while keeping legally required originals in a compliant accounting or document system.
Technical boundaries for information barriers
Issue isolated Agent Tokens per transaction to support, rather than replace, organizational information-barrier controls.
See the whitepaper for the full design and technical model
It covers control design for AI-era sharing, encryption protocol choices, Agent Token design, audit-log structure, FISC-aligned governance detail, and how Slack can be governed as a next delivery path.
Rollout steps
Three steps to connect finance AI agents with Sealith
Step 1
Start with one AI job
Pilot Sealith handoff inside an existing flow such as KYC screening or month-end close. No card required, 14-day free trial.
Step 2
Automate with Agent Token and API
Use Business REST API and Agent Token to automate agent startup, file fetch, and audit logging. MCP also supports direct operation from Claude Desktop.
Step 3
Expand into a company-wide AI governance layer
Separate scopes by department and let CFO and compliance teams oversee which AI accessed which materials in real time.
Plans
Adoption cost for a governed finance-AI layer
Start free, then move to Business when finance-agent integration becomes necessary.
Free
Try the basics of encrypted transfer and audit logging on a small volume of finance materials.
Start freeStarter
For one operator managing external document delivery with open tracking, CSV export, and immediate revoke.
Start free trialTeam
Standardize sharing rules across compliance, finance, and corp dev with multiple admins and organization-level audit logs.
Start free trialBusiness
Control the Sealith handoff boundary for financial AI agents through REST API, Agent Tokens, MCP, and audit export.
Start free trialStarter and above can issue referral links. When a referred user upgrades to a paid plan, credits are applied automatically to the next invoice.
FAQ
Finance AI agents × Sealith FAQ
Overview
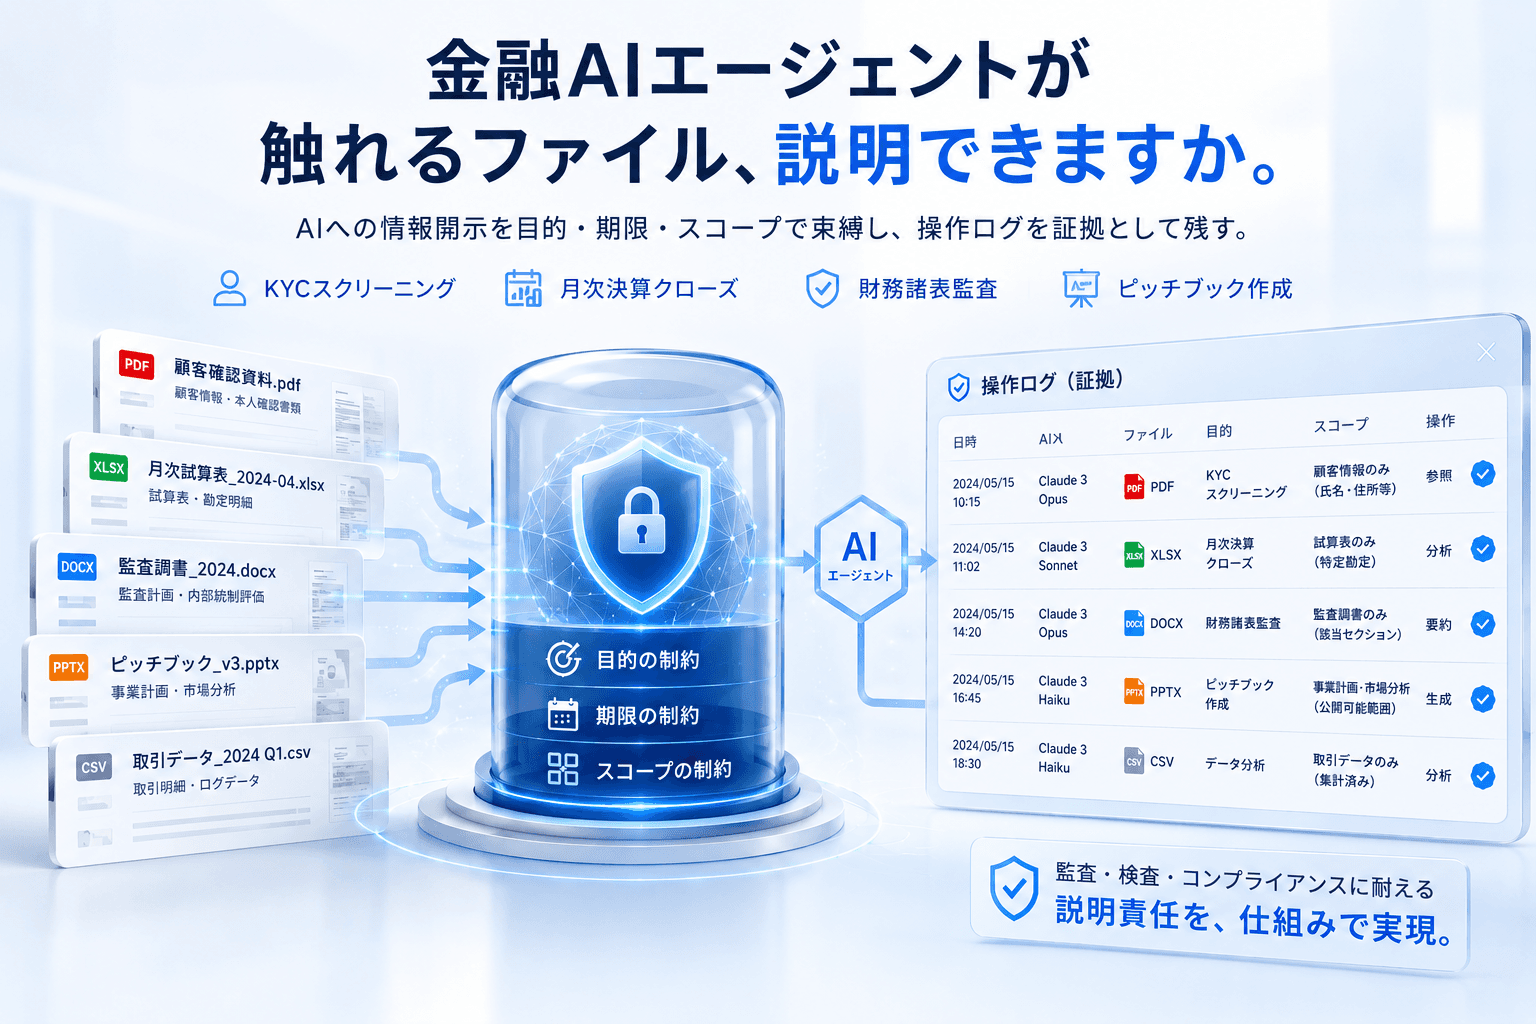
You may reuse this image in internal review or proposal documents.
AI Work Governance to Agent Commerce
Provenance for what AI creates. Approval for what AI releases. Recovery for what AI transacts
AI disclosure controls connect to a transaction mandate, price locking, JPYC payment attribution, and a canonical ledger for fulfillment, cancellation, and refunds.
AI WORKSPACE / HARNESS
AI thinks and builds
Cloudflare OS, Gemini, Copilot, OpenClaw, or your own agent
AI WORK PASSPORT / RELEASE CONTROL
The company releases the work
Delegation, provenance signals, asset binding, policy, and human approval
SEALITH TRANSACTION BOUNDARY
The company delegates
Purpose, accountable entity, budget, quote, approval, and idempotency
PROVIDER / PAYMENT RAIL
The outside world fulfills
OnePlace, eSIM, JPYC, and future providers — reconciled through recovery
Make finance-AI explainability enforceable with Sealith
Combine finance-agent automation with strict information control so efficiency and audit readiness can coexist.
No credit card required · 14-day free trial · Cancel anytime